Category: Compliance
-
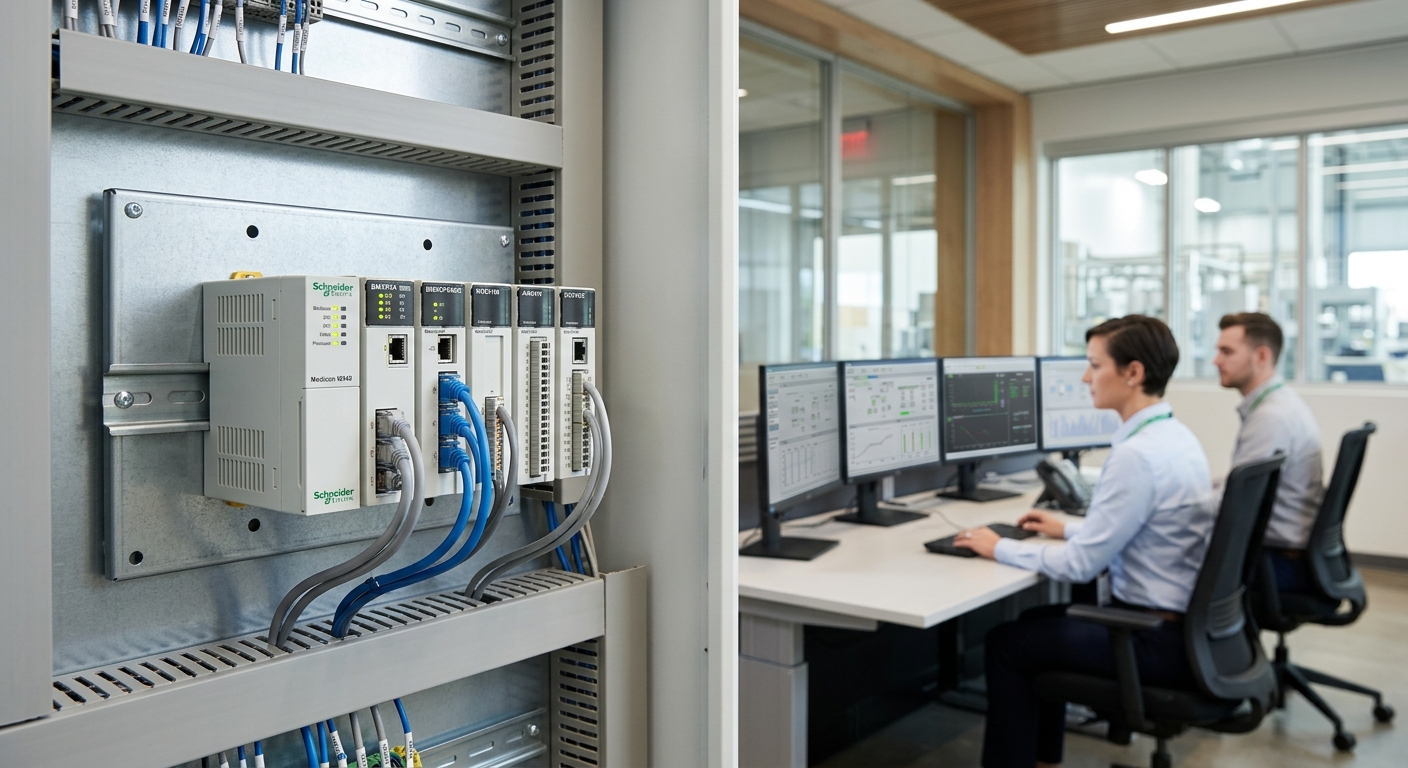
Schneider Electric Modicon M340 Controller and Communication Modules
When the Cybersecurity and Infrastructure Security Agency released an advisory about a vulnerability in Schneider Electric’s Modicon M340 controllers and a suite of...
-
Using Cyber Decoys to Strengthen Detection and Response
Regulated and defense‑contractor enterprises have long faced a paradox: the more stringent the compliance requirements, the more attractive the environment becomes to...
-
CMMC News & Updates: Latest CMMC Changes for Defense Contractors
In the fast‑moving world of defense procurement, the Department of Defense’s Cybersecurity Maturity Model Certification (CMMC) remains the single most critical compliance...
-
CMMC implementation plan takes shape in proposed rule | News Brief | Compliance Week
When the Department of Defense released its draft guidance for the next generation of the Cybersecurity Maturity Model Certification, the industry’s attention turned immediately...
-
The digital front door to government has moved. Most agencies don’t know it yet
When the federal government’s primary point of contact with the public migrated from a web‑based portal to an AI‑powered conversational interface, the ripple effect was...
-
Pentagon Suspends CMMC Phase 2 Requirements and Launches Review of Cybersecurity Certifica
The U.S. Department of War announced on the 13th of July, two thousand and twenty‑six that it would suspend the implementation of the second phase of the Cybersecurity Maturity...
-
CMMC Phase 2 Suspended: What Actually Changed for Your CMMC Level 2 Compliance Timeline |
The regulatory landscape governing federal supply chain cybersecurity shifted again on July Thirteen, Twenty Twenty Six, when the Department of War issued a CIO memo formally...
-
Veradigm Discloses Third Party Data Breach as Hackers Threaten to Publish Data
Veradigm disclosed a third party breach with attackers threatening to publish data. What healthcare leaders should check across their supply chain.
-
Fair Work Commission condemns 'plain wrong' AI legal advice
The Fair Work Commission called an AI generated legal opinion plain wrong. Why regulated firms need governance, validation and human oversight.
-
DVIDS - Video - CMMC Phase II Suspended to Boost DIB Innovation
The Defense Department paused CMMC Phase Two to prioritize Defense Industrial Base innovation. What the suspension means for defense contractors.
-
Patient & Employee Data Exposed in Baylor Genetics Cybersecurity Incident
Baylor Genetics confirmed a cybersecurity incident exposing patient and employee data. What genomics and healthcare providers should change now.
-
Texas Hearing Institute Ransomware Attack Affects 30,000 Patients
Ransomware at Texas Hearing Institute exposed protected health information for nearly 30,000 patients. What it means for HIPAA risk and breach response.