
Cybersecurity Blog
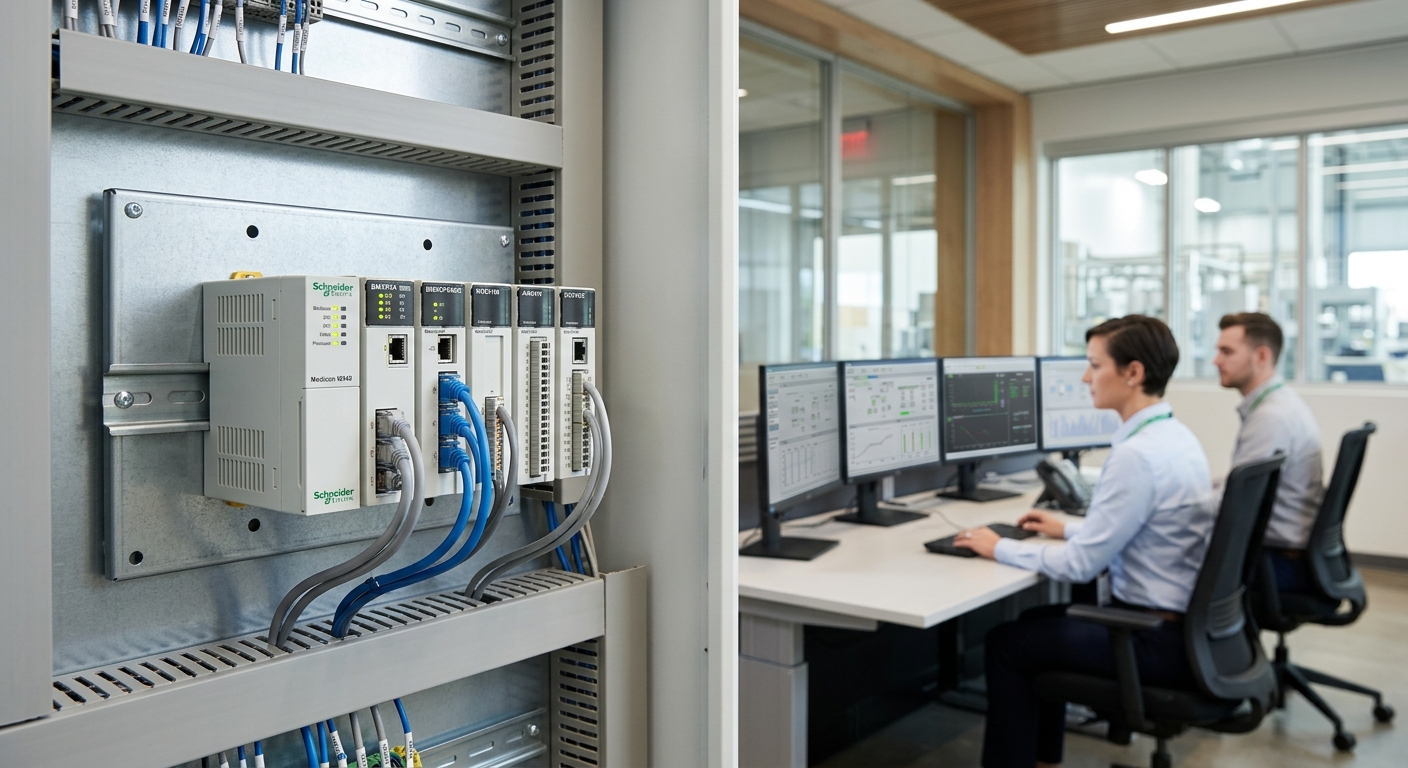
Schneider Electric Modicon M340 Controller and Communication Modules
Posted September 18, 2026 in Compliance, CMMC, NIST, HIPAA, Cybersecurity
When the Cybersecurity and Infrastructure Security Agency released an advisory about a vulnerability in Schneider...
New Check Point flaw lets hackers execute code with root privileges
Posted September 18, 2026 in Compliance, CMMC, NIST, HIPAA, AI
Check Point Software has announced a critical flaw that permits attackers to execute arbitrary code with root...
AI Contact Center QA Loops That Slashes Hallucinations Fast
Posted September 18, 2026 in AI, Compliance
AI Contact Center QA Loops That Cut Hallucinations Fast Hallucinations in contact centers show up as confident...
Using Cyber Decoys to Strengthen Detection and Response
Posted September 17, 2026 in Compliance, CMMC, NIST, AI, HIPAA
Regulated and defense‑contractor enterprises have long faced a paradox: the more stringent the compliance...
Cisco warns of max severity ISE zero-day exploited in attacks
Posted September 17, 2026 in Compliance, HIPAA, CMMC, NIST
Cisco has released a critical patch for a maximum‑severity vulnerability in its Identity Services Engine (ISE). The...
How Evidence-Backed Escalation Governance Keeps AI Support
Posted September 17, 2026 in AI, Compliance
Evidence-Backed Escalation Governance for AI Support Bots AI support bots can deflect a large share of routine...
CMMC News & Updates: Latest CMMC Changes for Defense Contractors
Posted September 16, 2026 in CMMC, Compliance, HIPAA, AI, NIST
In the fast‑moving world of defense procurement, the Department of Defense’s Cybersecurity Maturity Model...
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
Posted September 16, 2026 in Compliance, CMMC, HIPAA, NIST, Penetration Testing
In the past week, security researchers reported that a critical flaw in WSO2 API Manager - identified as...
Leadership Training for AI Era Risk and Accountability
Posted September 16, 2026 in AI, Compliance, Cybersecurity
Leadership Training for AI-Era Risk and Accountability AI is no longer a distant research topic, it’s showing up in...
CMMC implementation plan takes shape in proposed rule | News Brief | Compliance Week
Posted September 15, 2026 in Compliance, CMMC, AI, NIST, HIPAA
When the Department of Defense released its draft guidance for the next generation of the Cybersecurity Maturity...
Cisco patches Secure Email Gateway zero-day exploited in attacks
Posted September 15, 2026 in Compliance, CMMC, HIPAA, NIST, AI
When Cisco issued a patch for a zero‑day flaw in its Secure Email Gateway, the announcement reverberated far beyond...
Digital Sovereignty Exit Plans for AI Cloud Workloads
Posted September 15, 2026 in AI, Compliance, Cybersecurity, Managed Services
Digital Sovereignty Exit Plans for Cloud AI Workloads Digital sovereignty is about controlling where data lives,...